From L3/L4 to L7: How to Build a Multi-Layer DDoS Defense Architecture
Published on 2026-10-04|By ByteShield Team
Key takeaways
- Modern DDoS protection cannot be measured only by how much attack traffic it can absorb. It also needs different detection and mitigation methods depending on the Layer where the attack happens.
- Layer 1, DDoS Protection, handles abnormal Traffic, Packets, and Connections at L3/L4, focusing on BPS, PPS, SYN Rate, and Concurrent Connections.
- Layer 2, CC Defense, evaluates HTTP Requests and Request Patterns at L7, handling CC Attacks with custom rules, rate limiting, behavior-based verification, algorithmic signatures, and network-wide coordination.
- Layer 3, Bot Management, identifies Automated Traffic based on Client, Session, and Behavior. The goal is not to block every Bot, but to apply the right strategy for each type.
- The whole approach boils down to: Traffic → Request → Behavior.
In our previous article, "DDoS Attack Types Explained: From Volumetric Floods to CC and L7 Attacks", we explained that different DDoS attacks consume different resources.
Volumetric Attacks consume Bandwidth and Protocol Attacks consume Connections. At the Application Layer, HTTP Floods and CC Attacks can directly drain Web Server, API, or Database Resources.
So even when the end result is the same (a degraded service), the underlying problem can be completely different. A flood of UDP Traffic is usually a Network Layer problem, while a flood of Login Requests may keep draining Application Resources through HTTP Requests that look perfectly normal.
Modern DDoS protection cannot be measured only by how much attack traffic it can absorb. It also needs different detection and mitigation methods depending on the Layer where the attack happens. This is the core of a multi-layer defense architecture.
Why Might a Single Protection Mechanism Not Be Enough?
When an attack happens at L3/L4, a business may face huge volumes of Packets, Connections, or Reflection Traffic. When an attack moves to L7, the attacker may be sending Requests that fully comply with the HTTP Protocol.
For example, a POST /login could come from a real user, or from an Automated Client hammering the Login API. Looking only at the Network Layer, it is hard to tell whether these properly formatted Requests are putting the business at risk.
That is why different Security Mechanisms do not replace one another. Each handles a different layer of the problem:
- Network / Transport Layer: mainly monitors Traffic, Packets, and Connections
- Application Layer: extends the analysis to HTTP Requests, URIs, API Endpoints, and Request Rate
- More sophisticated Automated Traffic: requires deeper analysis of Client, Session, and Behavior
The purpose of a multi-layer defense is to make sure anomalies at each Layer are identified and handled at the right place.
Layer 1 (DDoS Protection): Handle L3/L4 Abnormal Traffic First
The first layer of a multi-layer defense deals with anomalies at the Network / Transport Layer.
A SYN Flood can exhaust Connection Resources through masses of unfinished connections, while attacks like UDP Floods, ICMP Floods, or DNS Reflection can generate huge volumes of abnormal Traffic in a short time. The main job of L3/L4 protection is to identify and handle these Network / Transport Layer Attack Patterns before the traffic can affect the Application.
ByteShield DDoS Protection covers the following attack types:
- Land Flood, ICMP Flood
- SYN Flood, SYN-ACK Flood, ACK Flood, FIN/RST Flood
- TCP Reflection, Connection Exhaustion
- TCP/UDP Fragmentation
- DNS Reflection / Amplification
It can also apply traffic control based on conditions such as GEOIP and Black/Whitelists, then further classify and handle traffic by Protocol, including ICMP, TCP, and UDP.
This layer focuses on BPS, PPS, SYN Rate, and Concurrent Connections. When these metrics show clear anomalies, the first priority is to confirm whether the Network / Transport Layer is under attack.
Layer 2 (CC Defense): At L7, Start Evaluating Requests
The absence of an obvious traffic spike at the Network Layer does not mean the service is not under attack.
At the Application Layer, an attack may take the form of a flood of HTTP Requests. Individually, requests like POST /login, GET /search, or GET /api/query may all look normal. But if they arrive in large numbers in a short time, or concentrate on high-cost Endpoints such as Authentication, Database Query, or Search, they can keep draining Application Resources.
L7 protection needs to go further and assess whether HTTP Requests and Request Patterns match normal business usage.
ByteShield CC Defense lets you build custom rules by combining multiple HTTP conditions, paired with actions such as rate limiting, behavior-based verification, and JS challenges. For APP and API scenarios, Requests can also be verified with algorithmic signatures, or combined with a Challenge Mechanism to strengthen Client Verification.
When attack sources are more distributed, an IP Blocklist alone may not be enough. CC Defense can also analyze anomalies through Request Patterns and behavioral characteristics, and use network-wide coordination so that identified CC Attack signatures and related defense policies take effect everywhere at once.
At this layer, the information being monitored expands from Traffic, Packets, and Connections to HTTP Requests, URIs, API Endpoints, and Request Frequency.
Layer 3 (Bot Management): From Requests to Understanding Behavior
In more complex L7 scenarios, evaluating individual Requests may still not be enough.
A real user, a legitimate Crawler, and a Malicious Bot can all send the same GET /product/123. If Automated Traffic also uses Distributed IPs, varied User-Agents and Request Intervals, or even mimics ordinary browsing flows, it becomes even harder to tell Clients apart using IPs or fixed Request Rules alone.
That is why L7 protection needs to extend from Request Analysis to Client and Behavior Analysis.
ByteShield Bot Management uses a library of known Bots and intelligent detection to classify different kinds of Automated Traffic, including partner Bots, monitoring Bots, aggregator Bots, malicious UA Bots, fake search engine Bots, and other known Automated Traffic.
But a Bot is not inherently malicious traffic. Search engines, Monitoring Services, and partner services can all generate legitimate and necessary Bot Traffic. So the goal of Bot Management is not to block every Bot. It is to first identify each Bot's type and behavior, then apply strategies based on business needs, such as monitoring, blocking, banning, human verification, or precise access control.
At this layer, the basis for decisions expands from individual HTTP Requests to Client, Session, and Behavior.
From Traffic to Request to Behavior: How Multi-Layer Defense Works
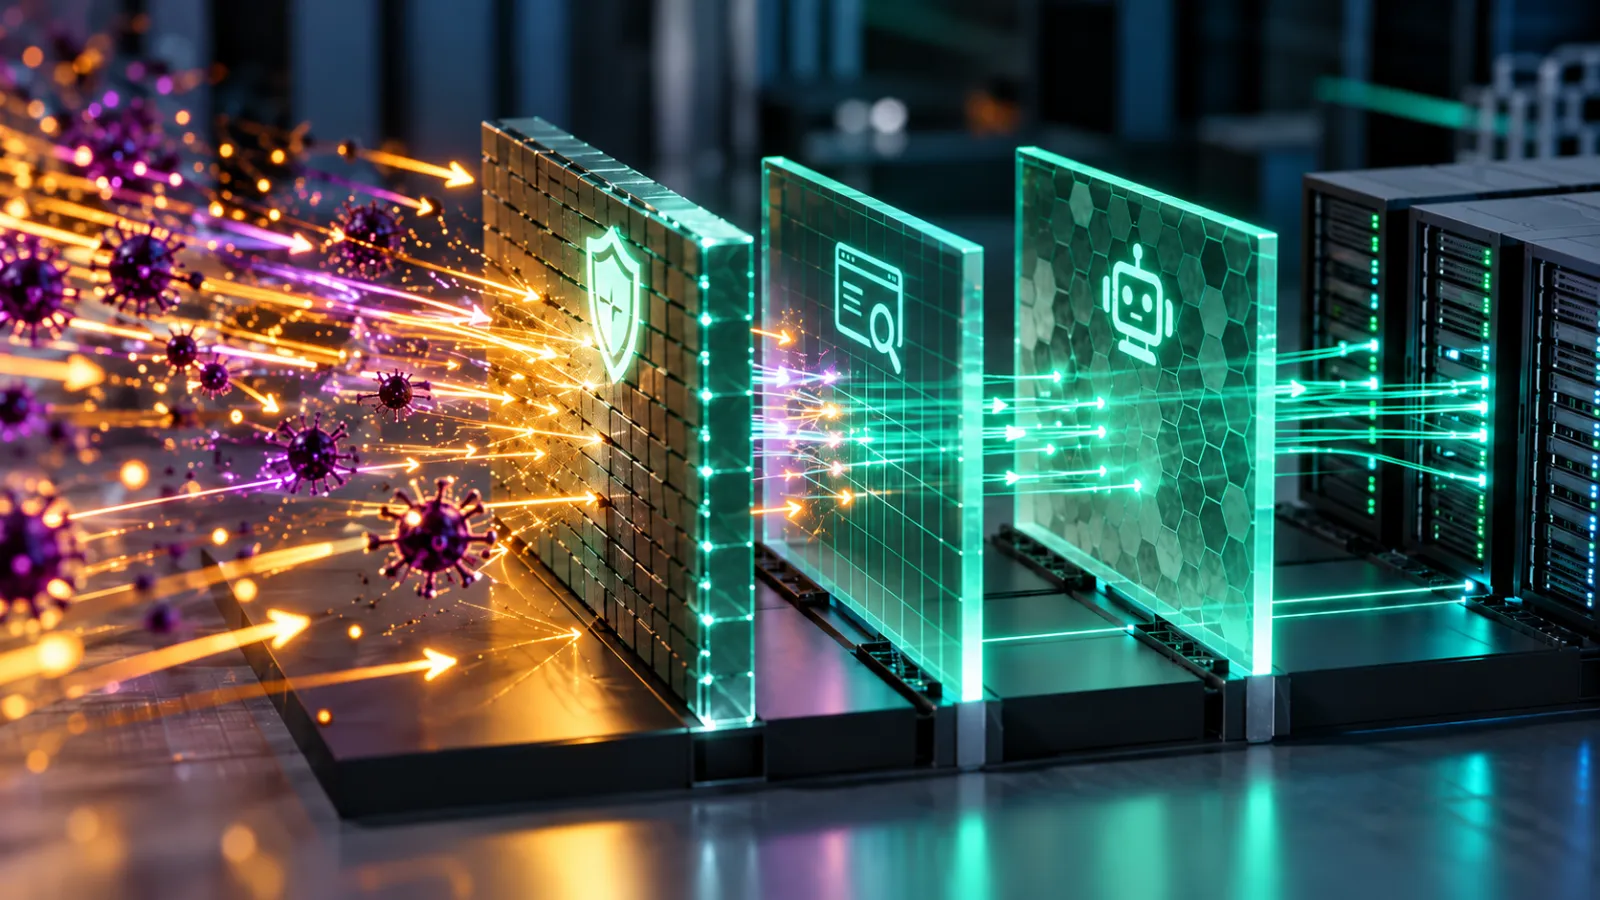
Put the three layers together, and you can see the overall logic of ByteShield's multi-layer defense:
| What you observe | Responsible layer | Mitigation focus |
|---|---|---|
| Large volumes of SYN, UDP, ICMP, or Reflection / Amplification Traffic | DDoS Protection | Handle L3/L4 Network / Transport Layer anomalies first |
| No obvious Network Traffic anomaly, but HTTP RPS is rising, or Requests are concentrated on /login, /search, /api/query | CC Defense | Analyze Request Patterns, Access Frequency, and Client Verification |
| Individual Requests look normal, but large amounts of similar Automated Behavior appear | Bot Management | Identify and manage based on Client, Session, and Behavior |
The whole approach boils down to: Traffic → Request → Behavior
In other words, it starts with traffic detection at the Network Layer, then extends step by step to Request Analysis at the Application Layer, and further to Behavior Analysis.
Multi-Layer Defense Does Not Mean Blocking All Traffic
The point of multi-layer protection is not for every Security Control to apply the same blocking logic.
Real Users, legitimate Crawlers, partner services, and Malicious Bots can all coexist in a website's traffic, so each Security Layer should handle the problems it is best placed to identify.
ByteShield DDoS Protection mainly handles abnormal Traffic, Packets, and Connections. CC Defense goes further, analyzing HTTP Requests, Access Frequency, and Client Verification. Bot Management applies different management strategies based on Bot Type and Behavior.
The closer you get to the Application and Business Layer, the more granular the information you need to understand.
From "Absorbing Traffic" to "Understanding Traffic"
Large Volumetric Attacks have not gone away, so Network Layer DDoS Protection remains an essential foundation of any security architecture.
But once an attack reaches the Application Layer, knowing how many Gbps you are absorbing is no longer enough. The signals a business needs to watch expand from BPS, PPS, and Connections to RPS, URIs, API Endpoints, Clients, Sessions, and Behavior.
L3/L4 looks at Traffic, L7 looks at Requests, and more sophisticated Automated Traffic requires a deeper understanding of Behavior.
ByteShield: Multi-Layer Security Protection from L3/L4 to L7
Every business faces different Traffic Patterns, Application Architectures, API usage, and business scenarios, so the Security Policies they need will differ too.
Through DDoS Protection, CC Defense, and Bot Management, ByteShield builds protection and management mechanisms across every layer, from Network Traffic and HTTP Requests to Automated Behavior, helping Web, APP, and API businesses reduce the impact of every type of Attack Traffic on their services.
The core of multi-layer protection is not just raising how much attack traffic you can withstand. More importantly, it is about adding detection capability layer by layer, so that each type of anomaly is caught and handled at the right Layer.
FAQ
Why might a single DDoS protection mechanism not be enough?
L3/L4 attacks mostly involve large volumes of Packets, Connections, or Reflection Traffic, while L7 attacks may consist of Requests that fully comply with the HTTP Protocol. Looking only at the Network Layer, it is hard to tell whether properly formatted Login or API requests are creating business risk, so you need mechanisms at different Layers, each handling the problems it is best placed to identify.
What do DDoS Protection, CC Defense, and Bot Management each handle?
DDoS Protection handles abnormal Traffic, Packets, and Connections at L3/L4, mainly monitoring BPS, PPS, SYN Rate, and Concurrent Connections. CC Defense analyzes HTTP Requests, URIs, API Endpoints, and Access Frequency at L7. Bot Management identifies and manages Automated Traffic based on Client, Session, and Behavior.
Will Bot Management also block search engine or partner Bots?
Not across the board. Bot Management first identifies a Bot's type and behavior, then applies strategies based on business needs, such as monitoring, blocking, banning, human verification, or precise access control. Legitimate Bot Traffic from search engines, Monitoring Services, and partner services can be allowed through.
How does CC Defense handle attacks from highly distributed sources?
When attack sources are distributed, an IP Blocklist alone may not be enough. CC Defense can analyze anomalies through Request Patterns and behavioral characteristics, verify Requests with algorithmic signatures in APP and API scenarios, and use network-wide coordination so that identified CC Attack signatures and defense policies take effect everywhere at once.
If you have related needs, explore ByteShield's security protection services, or contact the ByteShield team and we will recommend the right solution for your existing application architecture and business needs.