Using CDN as a Front-Line Load Balancer: Modern Traffic Distribution at Scale
Published on 2026-06-14|By ByteShield Team
Key takeaways
- Most sudden outages are not DDoS attacks but legitimate traffic spikes: a system designed for a few thousand users fails when tens of thousands arrive at once.
- Using a CDN as a front-line load balancer lets edge caching absorb more than 80% of traffic before it reaches your data center, leaving only core dynamic requests for the backend.
- With multiple origins, the CDN adds geo-optimized routing plus health checks and failover, switching traffic to a healthy origin within seconds so users notice nothing.
- For live and real-time services, intelligent traffic steering beats buying more bandwidth; whether a site survives the peak is decided at architecture design time.
When a website is suddenly flooded with requests, the first instinct for most teams is to ask: "Are we under a DDoS attack?"
In reality, many outages are not caused by malicious traffic at all. They happen because a system designed for a few thousand users is suddenly asked to serve tens of thousands, or even hundreds of thousands, at the same time. A large promotion, a popular live event, a new game launch, or a single viral social post can multiply traffic several times over in minutes.
If every request is blindly funneled to a single server or a single data center, the site will slow down, stop responding, or fail completely, even when there is no malicious traffic at all. This is why more and more companies are rethinking the role that traffic distribution and architectural elasticity play across their cloud environment.
The Real Culprit Behind Outages Is Rarely "Too Much Traffic"
Many people assume that adding more backend servers will solve any traffic problem. The reality is that once traffic enters the system, how those requests are distributed across resources is what actually determines service stability.
Imagine a restaurant that hires ten servers but funnels every customer through a single ordering counter. Queues and idle waiting still happen, while the staff in the back can only watch. Servers behave the same way. When some nodes are overloaded and close to collapse while others sit with plenty of idle capacity, overall compute power is never fully used.
Companies used to rely on a traditional load balancer to play the role of that "host who seats the guests." But in a world of high concurrency and global audiences, smart companies have pushed that line of defense all the way to the front edge of the network.
The Modern Answer: Using CDN as a Load Balancer
This is the architecture thinking that has gained so much traction recently: using the CDN (content delivery network) directly as a load balancer, the CDN as Load Balancer pattern.
A traditional load balancer is just a dispatcher. When heavy traffic arrives, it pushes the load to the backend, and the backend servers still bear all the pressure. A CDN, by contrast, has powerful edge caching. When millions of requests pour in, static resources such as images, page styles, and even some API responses are intercepted and served directly at the front-line CDN edge nodes.
That means more than 80% of traffic can be absorbed before it ever reaches your data center. What actually reaches the backend is only the core dynamic data, which dramatically reduces the load on the origin from the very start.
Multiple Origins and Cross-Region Steering Change How Traffic Is Managed
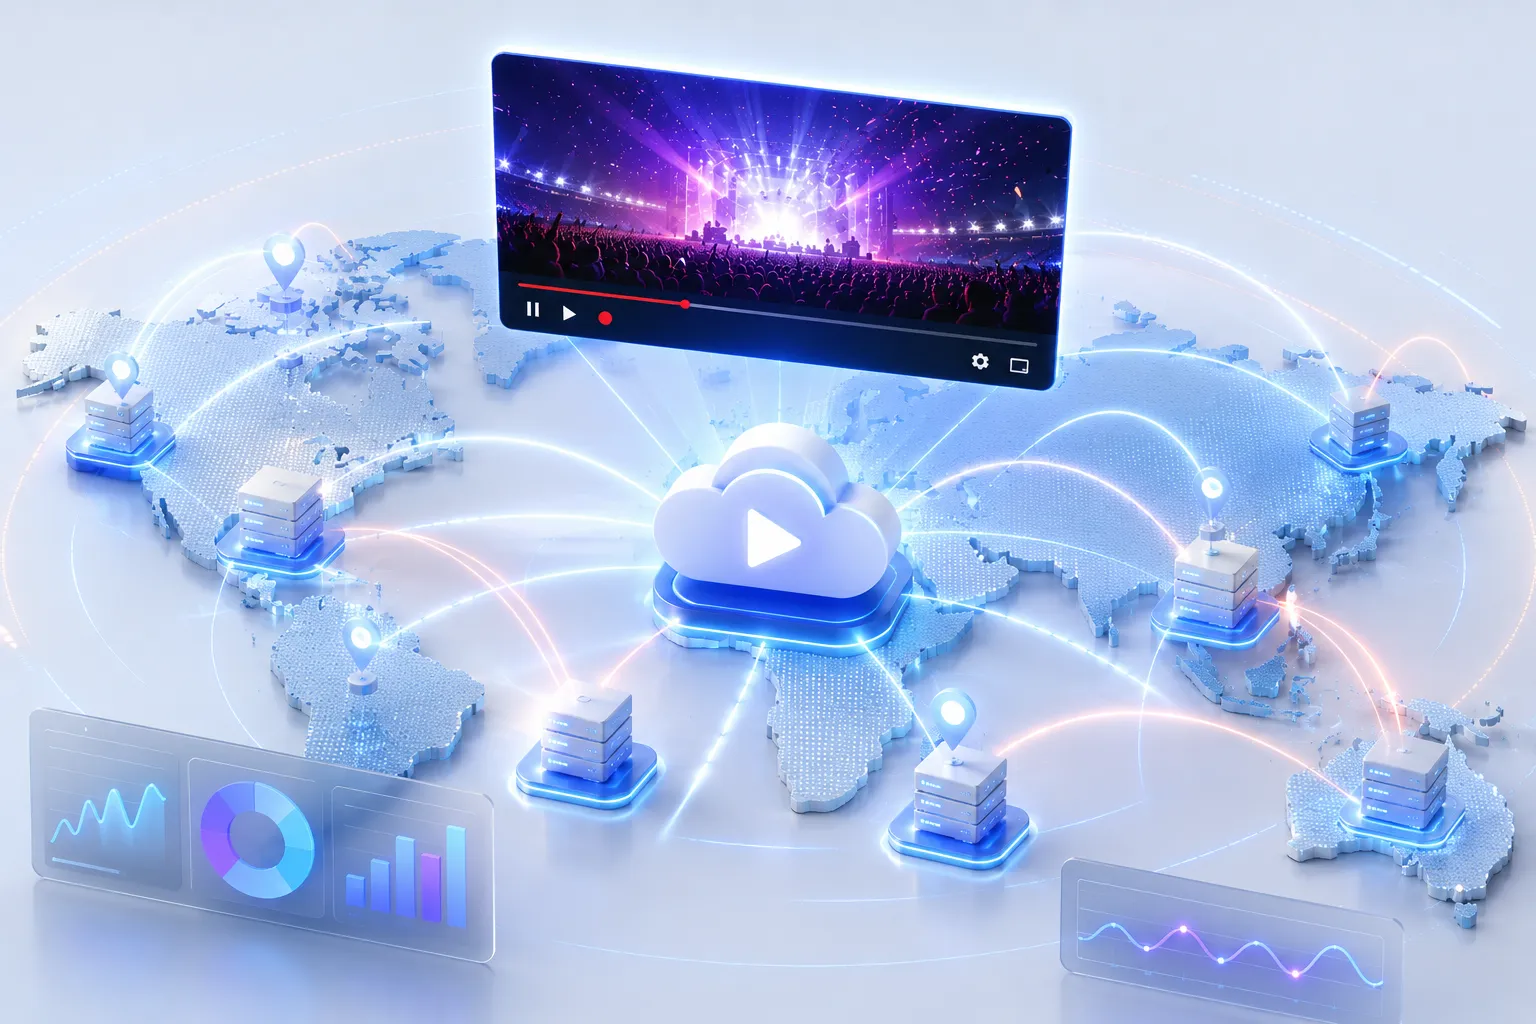
Building on CDN as a load balancer, modern companies take it a step further with a multiple-origin deployment strategy. When a service is deployed across several data centers or cloud environments at once, the CDN becomes the global traffic conductor.
When traffic arrives from around the world, the CDN can intelligently distribute it based on real-time conditions:
- Geo-optimized routing: users in Vietnam are routed to the Vietnam origin, users in Taiwan to the Taiwan origin, keeping latency to a minimum.
- Health checks and failover: if one region's origin goes down or becomes unreachable, the CDN switches traffic to a healthy origin within seconds, and users notice nothing.
This is why the modern idea of load balancing has merged with network security. Keeping attackers out matters, but what is even more valuable is keeping the service running through any abnormal event.
For Live and Real-Time Services, Traffic Steering Beats Buying More Bandwidth
When planning a large online broadcast, the first question many teams ask is "Do we have enough bandwidth?" Yet what really shapes the viewer experience is often the ability to route traffic and steer resources.
If some nodes are overloaded, viewers will still hit stutter, playback failures, or audio and video that fall out of sync, even when there is plenty of bandwidth left overall. For OTT platforms, sports broadcasts, iGaming, and real-time interactive applications, load balancing is not just a way to improve performance. It is the architectural core that keeps the service alive.
When an instantaneous traffic peak arrives, the ability to route users to the most suitable node as fast as possible is often far more effective than simply spending big on bandwidth.
Whether a Site Survives the Peak Is Decided at Design Time
When we assess site stability, we tend to look at how powerful the servers are and how much bandwidth there is. But what truly determines whether a business holds up in a traffic storm is whether that traffic is being managed effectively.
With CDN edge distribution combined with intelligent multi-origin steering, a company can keep users completely unaware even when traffic spikes or part of the origin fails. The most resilient architecture is never the one that promises nothing will go wrong. It is the one where your customers keep playing and keep checking out smoothly, even when something does.
If you are planning a large event, a live streaming service, a multi-cloud deployment, or global expansion, the ByteShield team can help you assess your current architecture, traffic distribution strategy, and cross-region deployment plan, so you can reduce the risk of traffic peaks ahead of time and build a more stable and scalable service.
FAQ
Is a sudden traffic spike always a DDoS attack?
Often not. Many outages are caused by legitimate traffic spikes: a large promotion, a popular live event, a game launch, or a viral social post can multiply traffic several times over in minutes, overwhelming a system designed for a few thousand users even when there is no malicious traffic at all.
How is using a CDN as a load balancer different from a traditional load balancer?
A traditional load balancer is just a dispatcher, so backend servers still bear all the pressure. A CDN intercepts static resources at its edge nodes, absorbing more than 80% of traffic before it reaches your data center, so only core dynamic requests reach the backend.
What happens when one origin fails in a multi-origin CDN setup?
The CDN runs health checks and, if one region's origin goes down or becomes unreachable, switches traffic to a healthy origin within seconds. Combined with geo-optimized routing, users notice nothing during the failover.
Talk to the ByteShield team and let us build an invisible moat around your architecture.